ghk cu how to take 7% GHK-CU ACCELERANT
Marsoni
M251S
Get it in 3 business days with 1 day shipping.
Friday, May 29
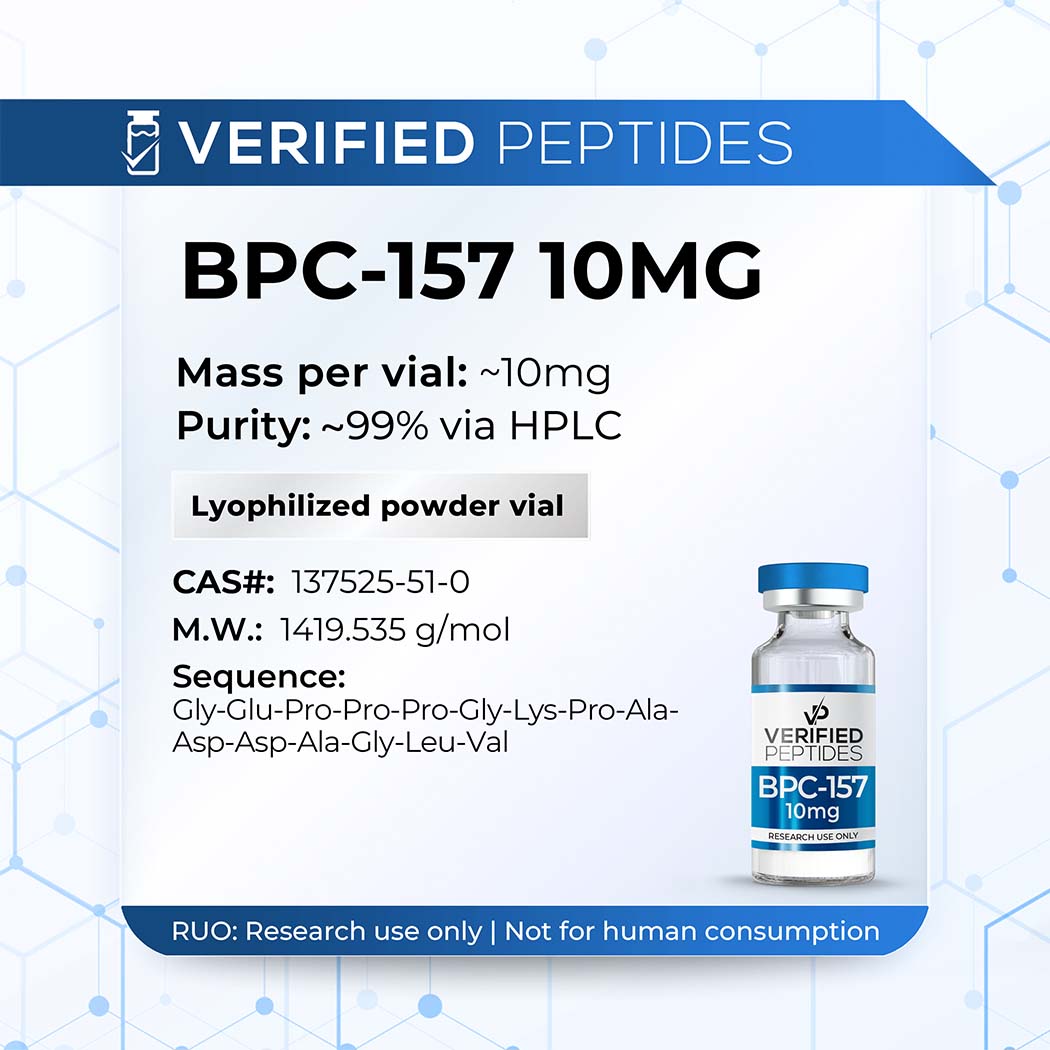
Efficacy of BPC 157 in murine wound healing compared to that of bFGF. Download Scientific Diagram gold seal bpc 157 CRE8 Compounding Pharmacy Supplements Hyper B12 MAGIC 10ml (Cyanocobalamin) Expiration date: July 2027 In diesem Video zeige ich dir, wie du mit einem optimierten Injektionsprotokoll fr TB 500 und BPC 157 deine Regeneration erheblich beschleunigen und deine Leistungsfhigkeit steigern kannst. Nach eingehender Analyse der gngigen Injektionsmethoden
Quick Dispatch:
Your ghk cu how to take 7% GHK-CU ACCELERANT orders ship within 1-2 business days.
Delivery Options:
- Standard: 3-7 business days
- Fast: 2-3 business days
- Express: 1-2 business days
Order Tracking:
You'll receive a tracking link by email once your ghk cu how to take 7% GHK-CU ACCELERANT ships.
Need Help?
Questions about ghk cu how to take 7% GHK-CU ACCELERANT, sizing, or delivery? We're just an email away.
Live Shipping Estimates:
Enter your location at checkout to see available shipping methods and costs for ghk cu how to take 7% GHK-CU ACCELERANT in your area.
Get Shipping Estimates
Exchange/Return Notes
- We offer a 30-day return/exchange service after receiving.
- Final sale items are not eligible for returns or exchanges.
- To process your return/exchange, please contact us at [email protected]
- Please click here for more details>>> Return & Exchange Policy
You may also like
4.4 ★★★★★
Based on 2453 reviews
Sort
Product Reviews
★★★★★ 5
Worth every penny
Format: Paperback
This book is in a class of its own compared to other security and pentesting books. I would highly recommend to anyone interested or currently working in network security. Instead of simply explaining how to use common pentesting tools, Wil Allsopp explains how they work and how to write your own custom tools from the ground up. Even if you do not have a programming background, it is worth understanding how an attacker can infiltrate a "secure" network without being detected.
WAS THIS REVIEW HELPFUL?YesReportShare
Reviewed in the United States on April 21, 2017
★★★★★ 4
The content itself though raises good points and does a good job outlining some more ...
Format: Paperback
Typos in the code make this a somewhat frustrating read. The content itself though raises good points and does a good job outlining some more advanced concepts
WAS THIS REVIEW HELPFUL?YesReportShare
Reviewed in the United States on January 8, 2018
★★★★★ 5
They aren't using crappy malware, so if you're InfoSec program is built ...
Format: Paperback
Bought yesterday, can't put it down -- will reread it again this week. This book is a solid gold mine on pulling our InfoSec heads out of our InfoSec tailpipes and focusing on the modes and methods our real adversaries are using. (Pro Tip: They aren't using crappy malware, so if you're InfoSec program is built on stopping malware you should be concerned.)
We all hear about the social engineering component to an effective attack, but to see it so effectively used over and over again with Wil's case studies really drives home the point.
If you're involved in either the management of an Information Security program, or involved in the more tactical parts of penetration testing, I'd put this on your short list of books to read this year. I hope he does a follow-up.
WAS THIS REVIEW HELPFUL?YesReportShare
Reviewed in the United States on July 10, 2017
★★★★★ 5
A well-written and updated book that covers Advanced Persistent Threats (APT) in detail.
Format: Paperback
The author truly knows his art. As a penetration tester, I feel that many books just re-hash the same old material and tools. This book covers much more than just pentesting, it covers APT and gives realistic scenarios and tools that actually work. This is a book for everyone who works offensive and defensive security because it covers how real malicious actors approach companies and steal their critical data.
WAS THIS REVIEW HELPFUL?YesReportShare
Reviewed in the United States on June 19, 2017
★★★★★ 5
Excellent Red Team InfoSec Book
Format: Paperback
One of the better books on the market on real penetration testing and creating advanced persistent threats. Great coding examples/strategies and how to think outside the box when it comes to attacking systems/companies. Elite guys like Wil Allsopp create their own custom tools all the time for real penetration testing. This is what nation-state actors are doing. Highly recommended.
WAS THIS REVIEW HELPFUL?YesReportShare
Reviewed in the United States on December 2, 2017
recommand products
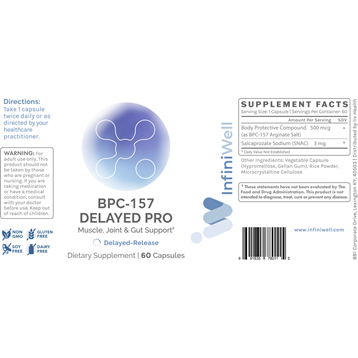
bulk bpc 157 BPC-157
26.11
best brand of oral bpc 157 BPC-157 PURE Oral Spray
28.48
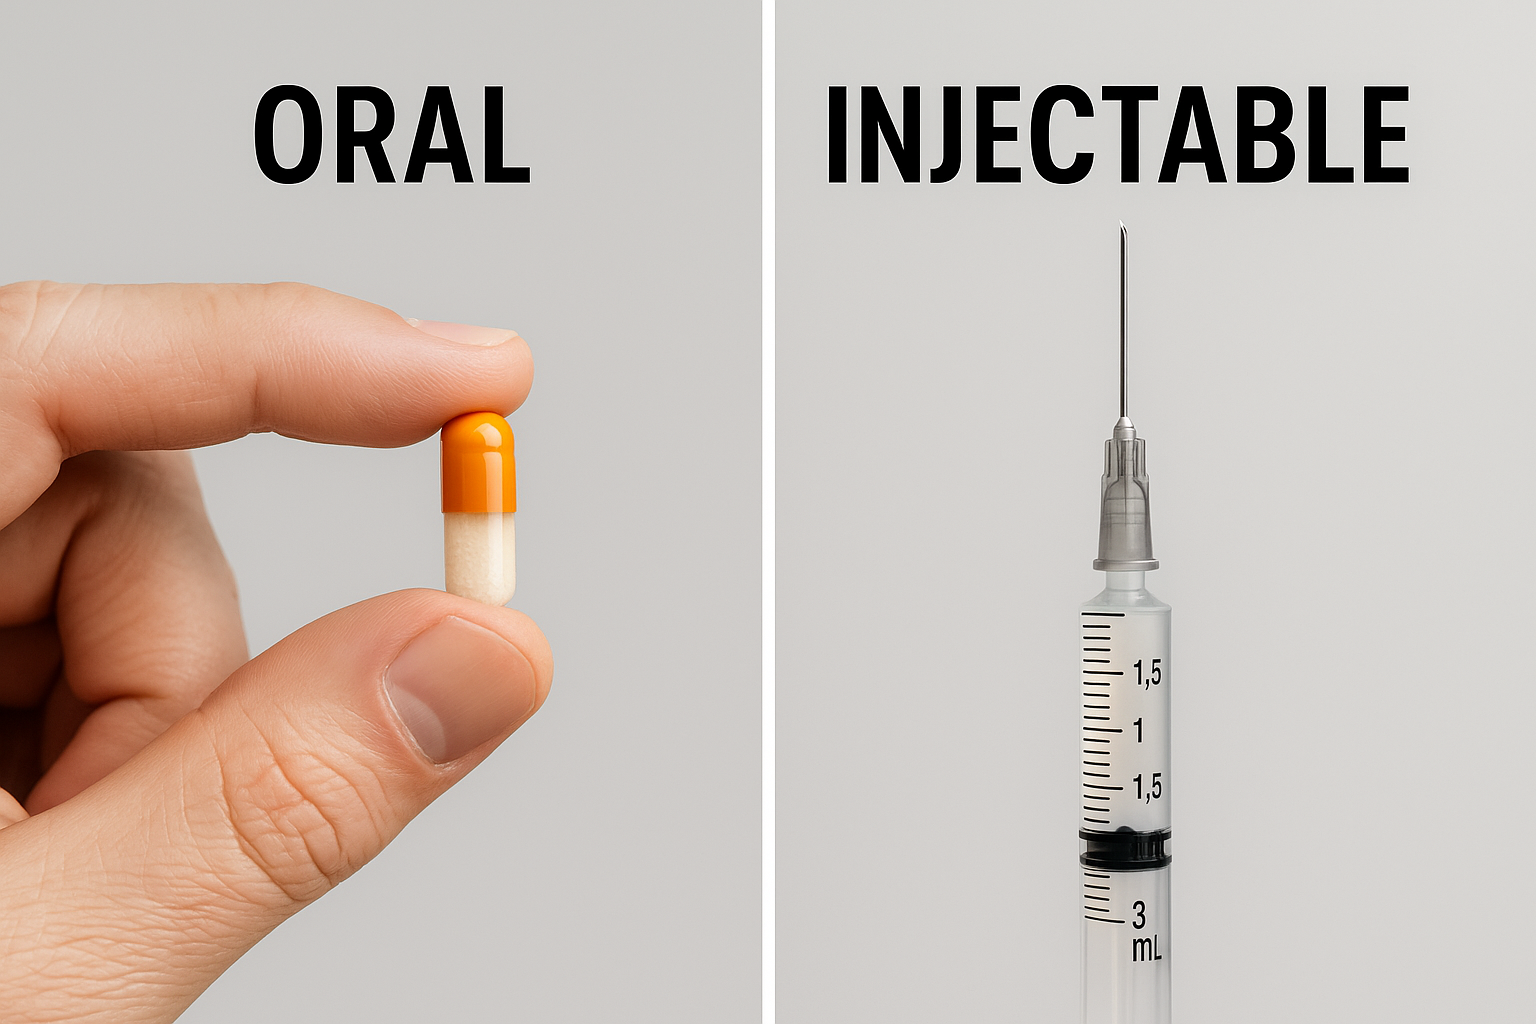
Oral vs Injectable BPC-157: Differences, Benefits, and When to Use Eac – Revolution Health & Wellness
26.89
bpc 157 how much should i take BPC-157 Peptide: Benefits, Dosage & Side Effects 2026
21.46
best brand of oral bpc 157 BPC-157 Pure Oral Spray, Integrative Peptides – Professional Supplement Center
24.42